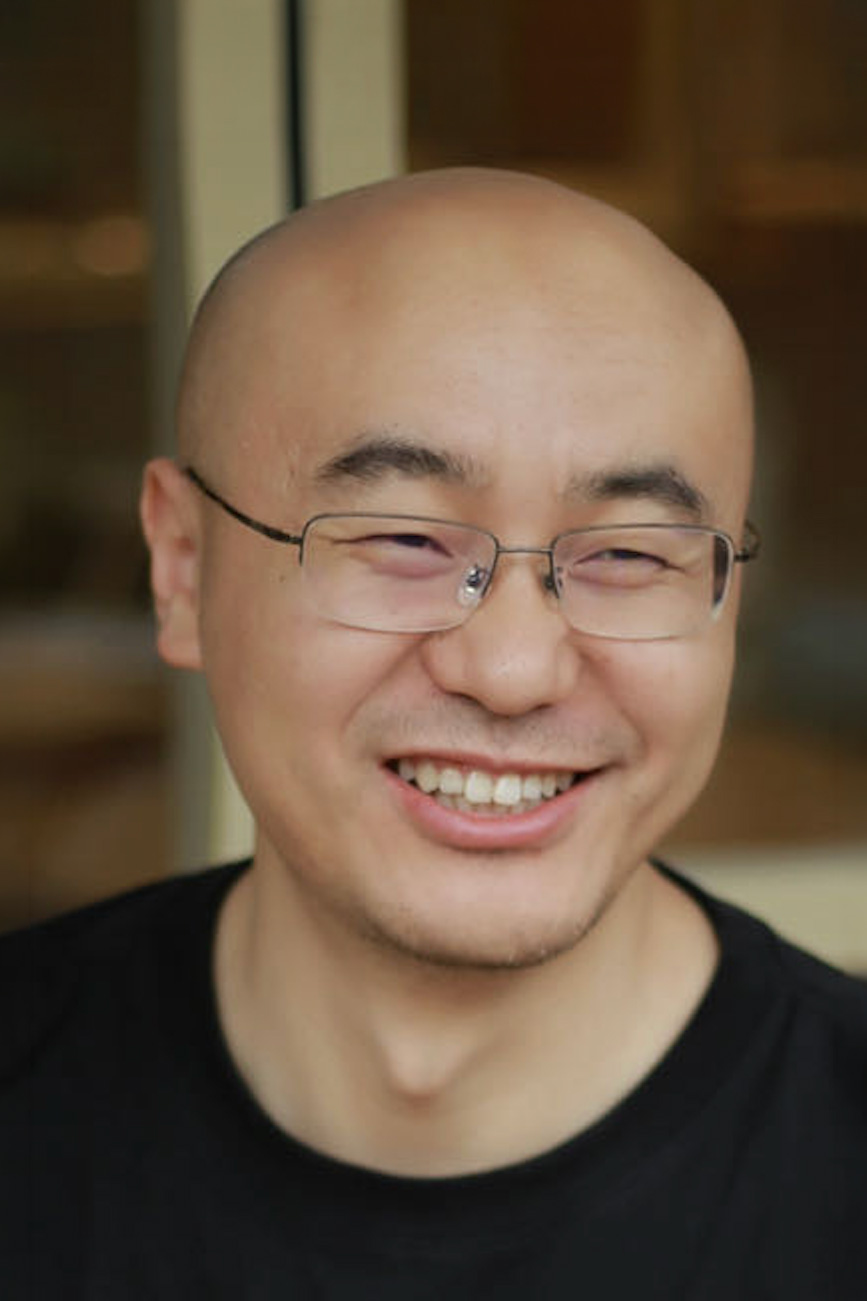
Yajin Zhou
Session Speaker
Dr. Yajin Zhou is an Associate Professor in the Department of Information Engineering at The Chinese University of Hong Kong (CUHK) and the Co-founder of BlockSec, a leading blockchain security and compliance company headquartered in Hong Kong. He earned his Ph.D. in Computer Science from North Carolina State University in 2015 under the supervision of Prof. Xuxian Jiang. Prior to joining CUHK, he served as a ZJU-100 Young Professor at Zhejiang University and previously worked as a Senior Security Researcher at Qihoo 360. Dr. Zhou's research focuses on building reliable and trustworthy computing systems, with expertise spanning operating systems, AI agent systems, blockchain infrastructure, and cybersecurity. His recent work explores secure system architectures for enterprise AI agents, trustworthy AI infrastructure, blockchain security, digital asset compliance, and cybercrime investigation. He has authored more than 70 publications in leading systems and security conferences, with over 11,000 Google Scholar citations and an h-index of 35. His contributions have been recognized with several prestigious honors, including the IEEE Symposium on Security & Privacy Test-of-Time Award (2026), the Most Influential Scholar Award in Security & Privacy, and recognition for one of his papers among the Top 100 Most Influential Security Papers Since 1981. Dr. Zhou actively serves the research community as a program committee member and reviewer for premier conferences, including IEEE Symposium on Security & Privacy, USENIX Security Symposium, ACM CCS, Financial Cryptography (FC), ACNS, and ASIACCS. His research has been translated into production systems that protect billions of dollars in digital assets while supporting regulators and law enforcement agencies worldwide.
Building Secure AI Agent Systems for EnterprisesLarge Language Models (LLMs) are rapidly evolving from conversational assistants intoautonomous AI agents capable of interacting with enterprise systems, executing workflows,accessing sensitive data, and making operational decisions. While these capabilities unlocksignificant productivity gains, they also introduce an entirely new security landscape thattraditional cybersecurity mechanisms were not designed to address.This talk presents a system-level perspective on securing enterprise AI agent systems. We firstexamine the emerging attack surface introduced by agentic AI, including prompt injection, toolabuse, memory poisoning, privilege escalation, indirect instruction attacks, and multi-agentmanipulation. These threats arise not only from the underlying language model, but also from theinteraction between agents, external tools, enterprise data, and execution environments.Building on these observations, the talk introduces a defense framework for enterprise AI agentsthat combines secure architecture design with runtime protection. The framework emphasizesleast-privilege authorization, capability-based tool access, trusted execution workflows,continuous risk assessment, policy-driven governance, and real-time monitoring of agentbehavior. Practical deployment considerations and lessons learned from securing production AIsystems will also be discussed.Finally, the talk outlines several open research challenges, including trustworthy autonomousagents, secure agent collaboration, AI-driven attack detection, and verification techniques foragentic systems. The goal is to provide both researchers and practitioners with a comprehensiveunderstanding of how to build AI agents that are not only intelligent, but also secure, reliable,and suitable for enterprise adoption.