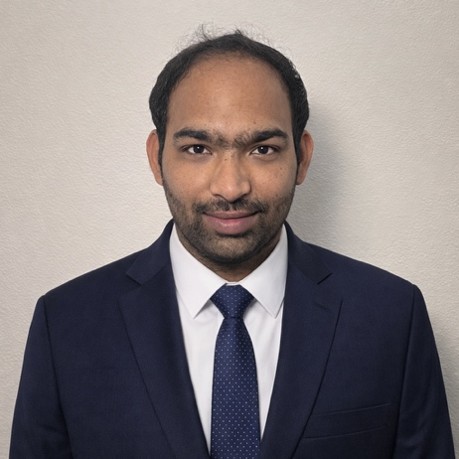
Harish Apuri
Session Speaker
Harish Apuri is a Software Engineer with experience building scalable, secure, and high-performance cloud and AI systems across finance, retail, and enterprise domains. He holds a Master's degree in Information Technology and Management from The University of Texas at Dallas and a Bachelor's degree from Jawaharlal Nehru Technological University, Hyderabad. His expertise spans MLOps, Infrastructure-as-Code, Kubernetes, and multi-cloud platforms including AWS, Azure, and Google Cloud. His research focuses on agentic AI, autonomous cloud operations, and intelligent infrastructure security, with multiple peer-reviewed publications in IEEE, Springer, and Q4-indexed venues covering AI-driven root-cause analysis, multi-agent autonomous workflows, and self-healing infrastructure using LLM agents. He has completed 65 peer reviews, served as a publication chair and main editor, and received a Best Paper Award
Agentic AI for Autonomous DevOps: From Predictive Vulnerability Detection to Self-Healing Cloud Infrastructure
Abstract
Modern CI/CD pipelines ship code multiple times a day, yet the security tooling most organizations rely on SAST, DAST, container scanners, and manual review gates — remains reactive, rule-bound, and blind to novel misconfiguration or attack patterns. This body of work presents a coordinated set of multi-agent AI frameworks that shift cloud-native security from periodic scanning toward continuous, closed-loop, self-correcting assurance. Across five studies, specialized agents built on Graph Attention Networks, Transformer risk heads, Deep Q-Network reinforcement learning, and fine-tuned Code Llama generative models are combined to predict, priorities, remediate, and enforce security posture across the full commit-to-runtime lifecycle, spanning Infrastructure-as-Code, containers, CI/CD pipelines, and multi-cloud deployments. The frameworks were evaluated on real and synthetic corpora exceeding 48,000 IaC templates, 47,800 multi-cloud deployment events, and 156,000 production security events across AWS, Azure, and GCP. Results demonstrate misconfiguration- and vulnerability-detection F1-scores between 0.93 and 0.95, Mean-Time-to-Detect reductions of 85–95%, Mean-Time-to-Remediate reductions of 61–87%, false-positive reductions exceeding 60–80% relative to rule-based baselines, and security-incident cost reductions of up to 92% in controlled deployment simulations, alongside measurable improvements in Zero-Trust posture and IAM least-privilege compliance. Statistical testing across paired and non-parametric designs confirmed these gains as significant and practically meaningful. The talk will walk through the shared architectural pattern underlying these systems — perception agents, risk-scoring agents, generative remediation agents, and human-in-the-loop autonomy gates — and discuss governance, explainability, and adversarial-robustness challenges that remain before such agentic pipelines can be trusted with full autonomous enforcement in production environments.